FREE DOWNLOAD · SHARE ANYWHERE

CVE timeline share cards — cybersecurity news you can share

One picture that tells the whole story: disclosure → patch → days it took. Download a card, post it, and every share carries the link to the free 30-second exposure checker. All dates sourced from the checker pages on this mirror.

What are CVE timeline share cards for cybersecurity news?

CVE timeline share cards are free graphics that turn cybersecurity news into one shareable picture: each card shows when a vulnerability was disclosed, when a patch shipped, and how exploitation unfolded, and every card links readers to the matching free exposure checker so they can test their own systems in 30 seconds.

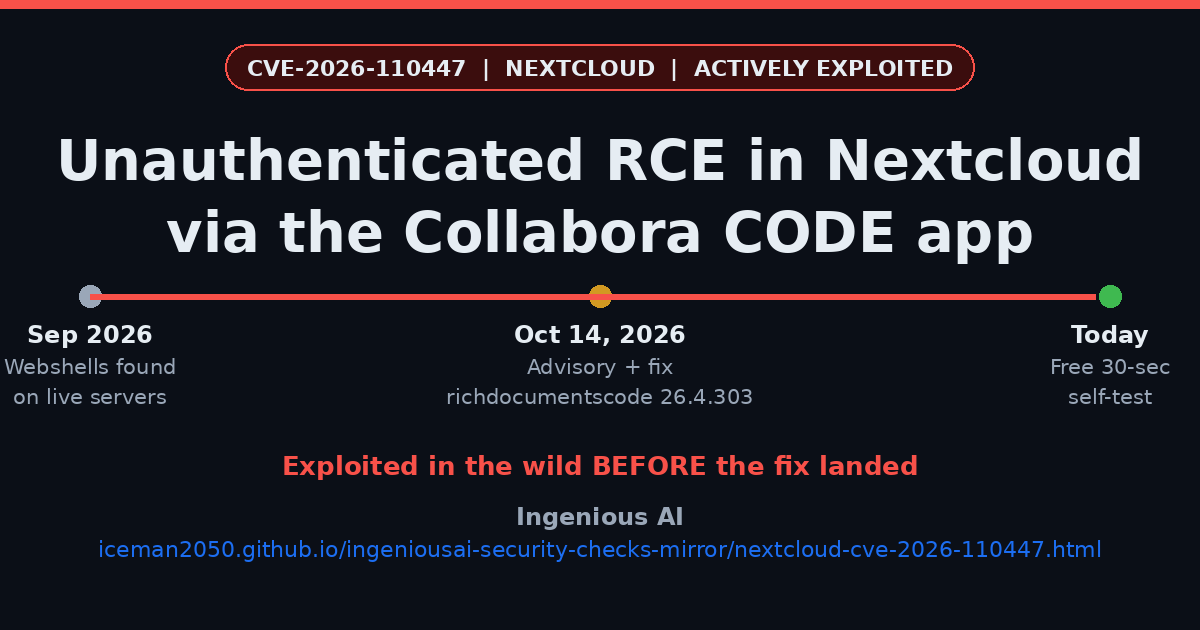
Nextcloud CVE-2026-110447 — webshells before the fix

Unauthenticated RCE via the Collabora CODE Server app · fix: richdocumentscode 26.4.303

Timeline of Nextcloud CVE-2026-110447: webshells on live servers since September 2026, advisory and fix October 14 2026
<a href="https://ingeniousai-security-checks-mirror-0e97b6.gitlab.io/nextcloud-cve-2026-110447.html"><img src="https://ingeniousai-security-checks-mirror-0e97b6.gitlab.io/share-cards/nextcloud-cve-2026-110447.png" alt="Nextcloud CVE-2026-110447 timeline — free 30-second exposure check by Ingenious AI"></a>

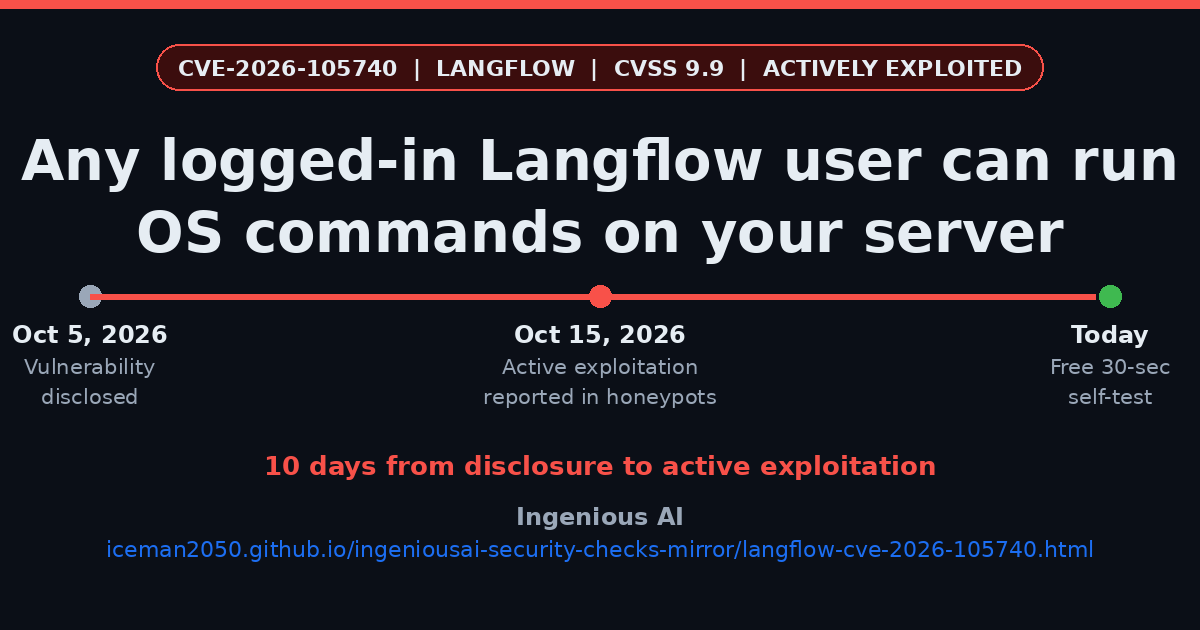
Langflow CVE-2026-105740 — 10 days to active exploitation

Logged-in user → OS commands via MCP stdio transport · CVSS 9.9

Timeline of Langflow CVE-2026-105740: disclosed Oct 5 2026, active exploitation reported Oct 15 2026
<a href="https://ingeniousai-security-checks-mirror-0e97b6.gitlab.io/langflow-cve-2026-105740.html"><img src="https://ingeniousai-security-checks-mirror-0e97b6.gitlab.io/share-cards/langflow-cve-2026-105740.png" alt="Langflow CVE-2026-105740 timeline — free 30-second exposure check by Ingenious AI"></a>

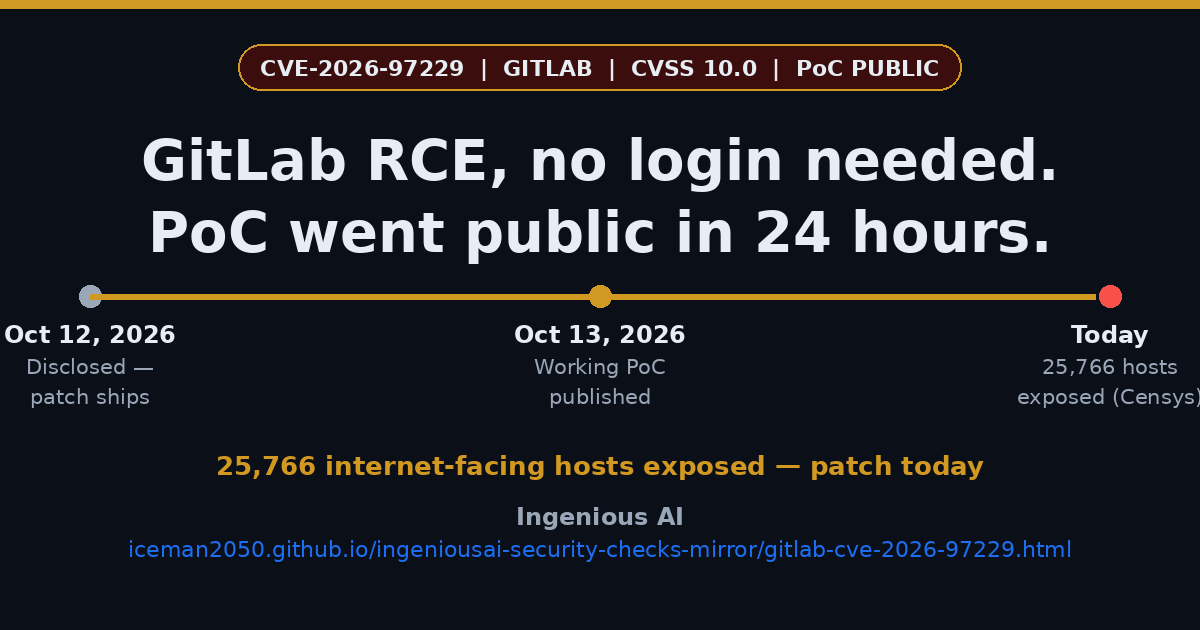
GitLab CVE-2026-97229 — PoC public in 24 hours

CVSS 10.0 RCE, no login needed on open instances · 25,766 hosts exposed per Censys

Timeline of GitLab CVE-2026-97229: disclosed Oct 12 2026, PoC public Oct 13 2026, 25766 exposed hosts
<a href="https://ingeniousai-security-checks-mirror-0e97b6.gitlab.io/gitlab-cve-2026-97229.html"><img src="https://ingeniousai-security-checks-mirror-0e97b6.gitlab.io/share-cards/gitlab-cve-2026-97229.png" alt="GitLab CVE-2026-97229 timeline — free 30-second exposure check by Ingenious AI"></a>

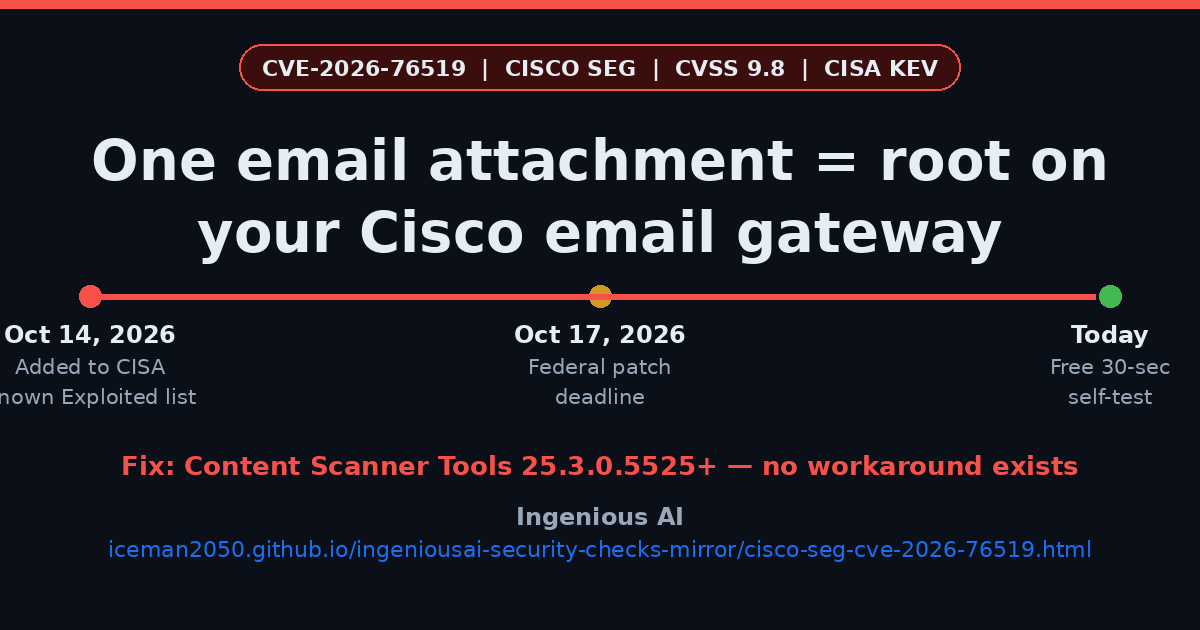
Cisco SEG CVE-2026-76519 — CISA KEV, no workaround

Unauthenticated root RCE via crafted email · CVSS 9.8 · federal patch deadline Oct 17

Timeline of Cisco SEG CVE-2026-76519: added to CISA KEV Oct 14 2026, patch deadline Oct 17 2026
<a href="https://ingeniousai-security-checks-mirror-0e97b6.gitlab.io/cisco-seg-cve-2026-76519.html"><img src="https://ingeniousai-security-checks-mirror-0e97b6.gitlab.io/share-cards/cisco-seg-cve-2026-76519.png" alt="Cisco SEG CVE-2026-76519 timeline — free 30-second exposure check by Ingenious AI"></a>

Frequently asked questions

Can I share these CVE timeline cards for free?

Yes — download any card and post it on X, LinkedIn, Reddit, forums or Slack. Every card carries the Ingenious AI watermark and the URL of the free exposure checker it describes.

Are the timelines accurate?

Every date comes from the matching free checker page on this mirror, which cites the vendor advisory, CISA KEV catalog or observed exploitation reports.

How do I embed a card on my blog?

Use the HTML embed snippet under each card — it wraps the image in a link to the free checker, so your readers can test their own systems in 30 seconds.
I have a question about this page